They Can't Attack
What They Can't See
Dispersive® Stealth Networking is a lightweight, quantum-resilient overlay that makes communications and data in motion invisible and keeps them running under attack. It strengthens the network and security stack you already run, with sovereign control of critical systems, enclaves, AI workloads, and distributed operations.

Resilient
Stay Operational When Everything Else Fails
Self-healing paths instantly reroute around jammed, degraded, or attacked connections. No failover events, no dropped sessions, and no downtime.

Sovereign Control
Command Your Network, Wherever It Resides
Set policy and control routing across infrastructure you don’t own or operate. Your enclaves, AI workloads, and mission systems stay governed by you, regardless of whose wires or clouds carry the traffic.

Performance
Ensure Critical Communications Under Any Conditions
Delivers stable, high-performance connectivity across cloud, hybrid, and edge environments, with no failover events, no performance collapse, and no operational downtime.
How Dispersive® Stealth Networking Works
Dispersive® Stealth Networking hides data in motion by splitting, encrypting, and obfuscating traffic across multiple diverse network paths simultaneously. Where VPN and SD-WAN rely on exposed tunnels and predictable routes, Dispersive removes them, eliminating the attack surface rather than trying to defend it. It extends your zero trust and SASE controls instead of competing with them.
Multi-Path Obfuscation
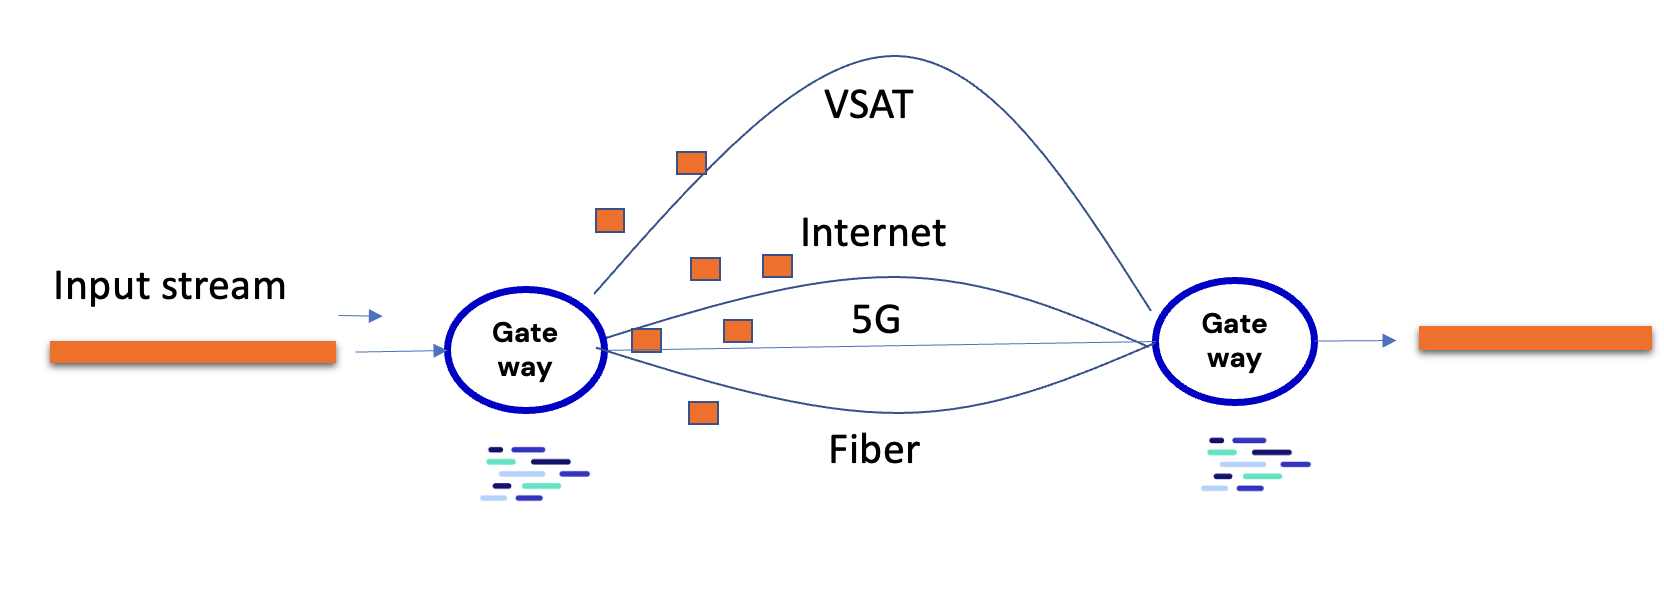
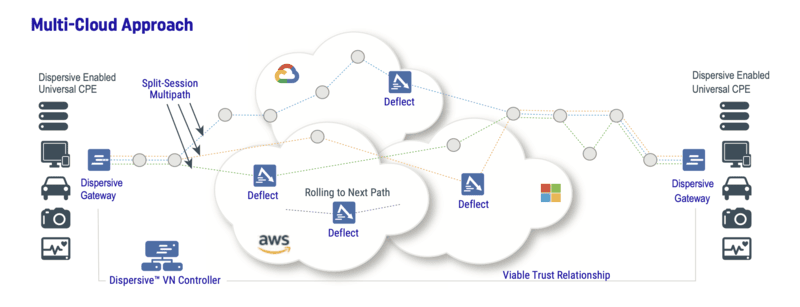
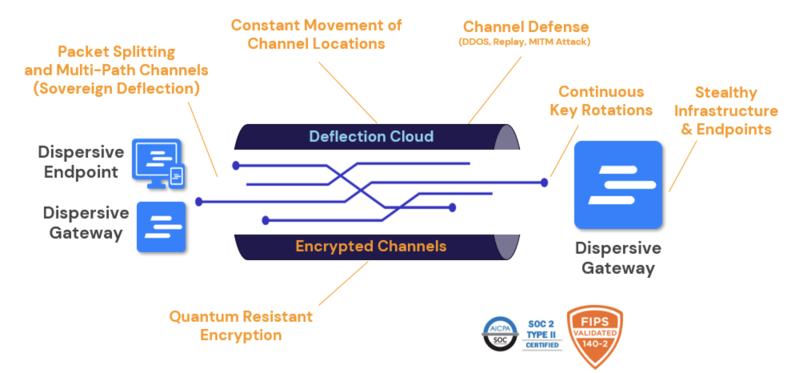
Dispersive® Stealth Networking breaks traffic into encrypted fragments and sends each piece across multiple channels and constantly shifting pathways. Because no full packet ever travels through a single route, there is nothing meaningful to intercept, correlate, or reconstruct. This defeats reconnaissance, renders packet capture useless, and removes observable flow patterns, eliminating the data-in-motion attack surface altogether.
Quantum-Resilient Encryption
Each fragment is protected with layered encryption, including NIST-standardized post-quantum algorithms ML-KEM and ML-DSA, using FIPS 140-3 validated cryptographic modules. Crypto agility lets algorithms change in one place rather than across every application and endpoint. A captured fragment is meaningless on its own, which limits what adversaries can harvest today to decrypt tomorrow.
Self-Healing Resilience
If a route becomes degraded, jammed, or attacked, Dispersive® Stealth Networking instantly shifts fragments across alternative channels without disrupting sessions or performance. This is Automated Moving Target Defense in practice: instead of defending a single path, the network continuously and autonomously repositions in motion, denying adversaries a fixed target to study or exploit. Preemptive cybersecurity by design delivers sustained uptime and throughput even under active attack, congestion, or infrastructure instability.
Trusted by Government, Critical Infrastructure,
and Global Enterprises
Proven in High Consequence Environments
Dispersive® Stealth Networking is recognized for advancing secure, resilient communications across government, critical infrastructure, and global enterprises. Our patented multipath architecture has been validated in mission-critical deployments where continuity, invisibility, and performance cannot fail, including a production edge deployment with American Tower in collaboration with Vertical Data.

Two Ways to Deploy Dispersive® Stealth Networking
Fortifying Networks with Secure, Resilient, and High-Performance Connectivity
DispersiveCloud®
DispersiveCloud® is a hosted SaaS deployment, SOC 2 Type II certified, that simplifies deployment and management without compromising performance or security. It runs on global cloud infrastructure from providers including Amazon Web Services and Azure for high availability.
DispersiveFabric™
DispersiveFabric™ is the self-hosted deployment, built for larger, more complex environments, where you run and control every component. A software-defined overlay network with a microservices architecture, DispersiveFabric™ deploys on the infrastructure you choose; public cloud, private cloud, containers, VMs, or dedicated hardware.

Stay Ahead with Expert Insights
Stay informed with expert analysis, best practices, and deep dives into the latest cybersecurity challenges and developments to strengthen your security posture.